Wales, working UK-wide
We are Tarian Labs.
A team of practitioners who spent their careers defending the UK's most sensitive systems, now doing it for businesses that cannot afford to get this wrong.
Our origins
Built by practitioners who know what it actually takes to stop a determined attacker.
Tarian Labs was founded by practitioners from UK defence and critical national infrastructure. The kind of environments where the consequences of getting it wrong are measured in national impact, not SLA breaches.
What those practitioners kept seeing was a widening gap. Governments and large enterprises had the resources to build serious security programmes. Scaling businesses did not. They were being sold automated scans dressed up as penetration tests, compliance checklists passed off as real assurance, and point-in-time reports that were out of date before the ink dried.
Tarian was built to fix that. We take the rigour, the methodology and the practitioner mindset from the highest levels of UK cyber defence and apply them to businesses that are growing fast and cannot afford to get this wrong.
Tarian Labs is entirely UK-owned and operated. Our practitioners hold UK government-recognised certifications, all engagement data is held onshore under UK jurisdiction, and we answer to no one outside the UK. In an era where the provenance of your security partner is a compliance question as much as a commercial one, that matters.
The founders
One of us builds. One of us breaks.
Most testing companies only bring the second half. It is the reason our findings come with a way forward, and not just a severity rating.
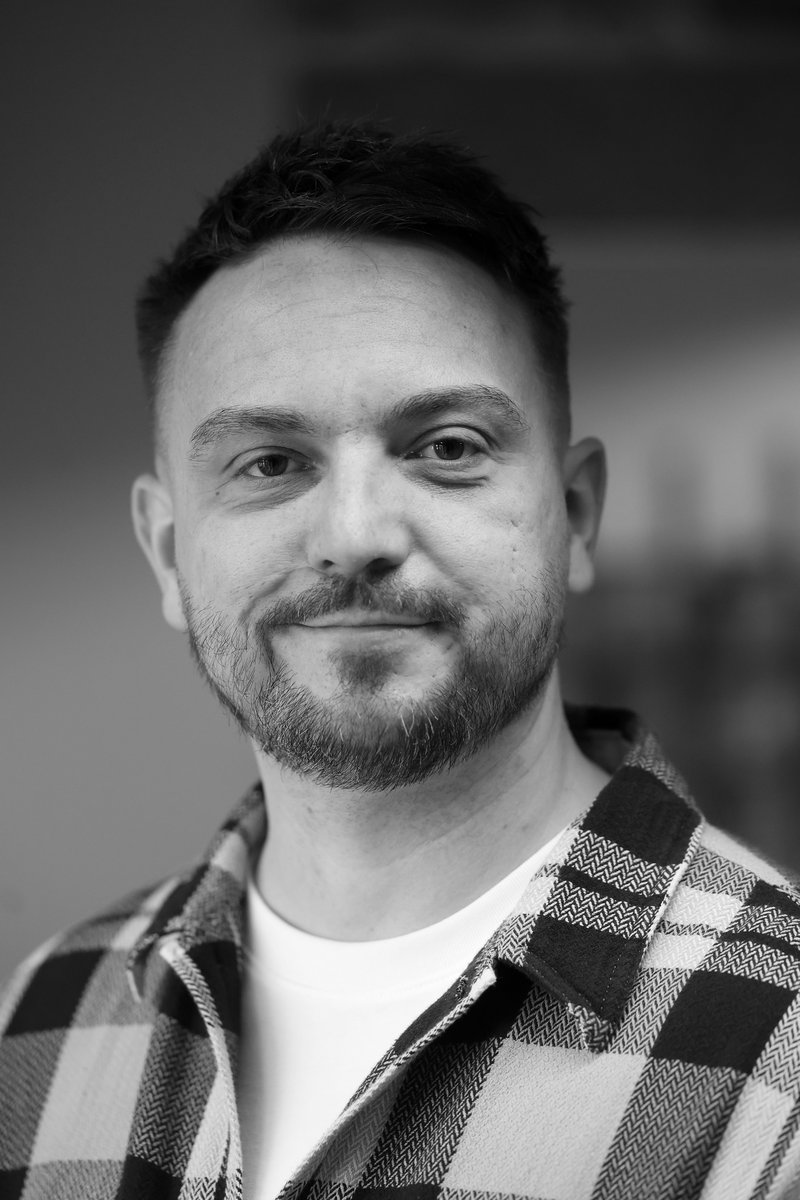
Kevin Hanford
Co-founder and CEO
He built the systems that had to hold.
Twelve years in UK defence and Critical National Infrastructure, building and validating high-assurance security products used across government. In that world you do not get to patch your way out of a design mistake. Systems are expected to hold against a determined, well-resourced attacker for years, and the assurance work happens long before anything reaches production.
Kevin's discipline is security by design: secure architecture, secure development, and validation that proves a control does what it claims to do. It is the opposite of the bolt-it-on-afterwards approach most businesses inherit by default.
He leads the commercial side of Tarian Labs, from scoping through to client relationships and partnerships. That background is why our reports do not stop at the problem. Knowing how something should have been built in the first place is what turns a finding into something your engineers can act on.
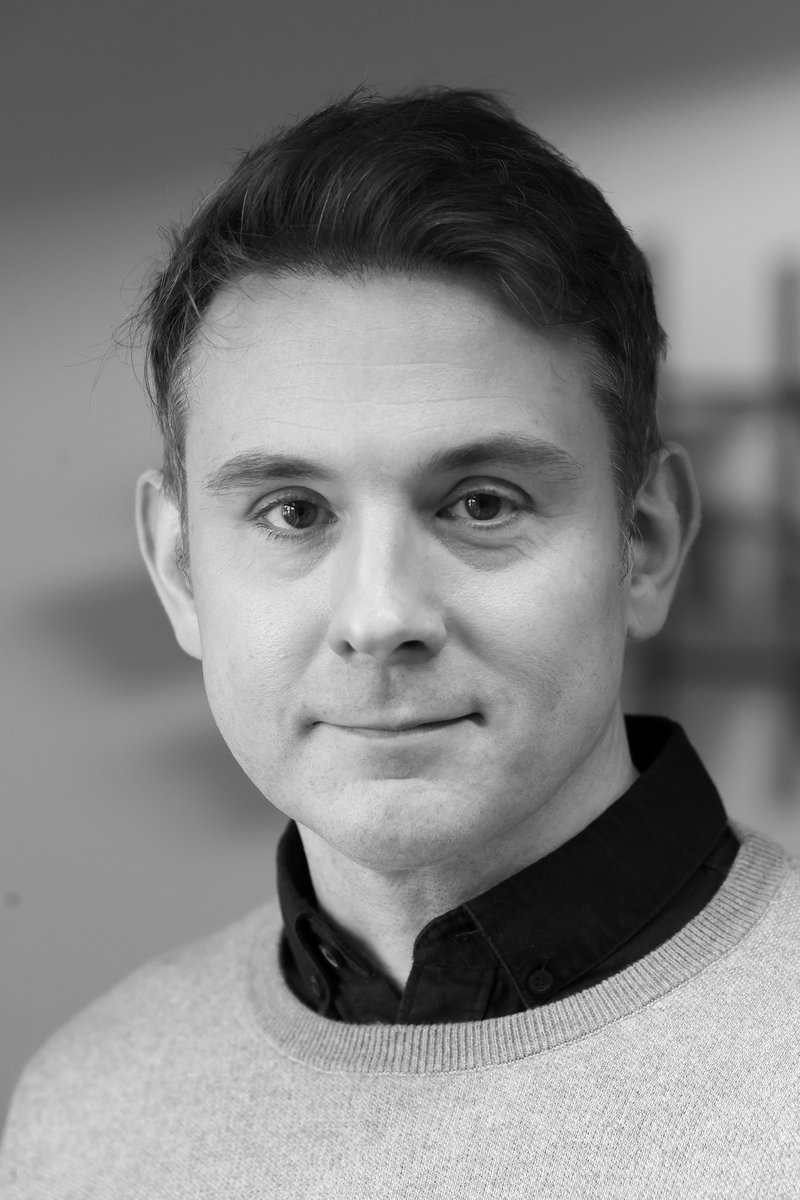
Marc Hill
Co-founder and Head of Technical Delivery
He finds the point where they don't.
Ten years across UK government, defence, and Critical National Infrastructure. Penetration testing, red team adversarial simulation, and CNI security, against targets where a missed weakness has national consequences rather than commercial ones.
Marc holds CSTL-INF, examined by The Cyber Scheme, one of only two bodies certified to examine against UK Government penetration testing standards. It is recognised by the NCSC, and by the UK Cyber Security Council as qualifying for Principal and Chartered status. He is among a small number of practitioners in the UK certified at that level.
He leads all technical delivery and signs off every Tarian Labs engagement. Every finding is traced, validated, and confirmed by a practitioner before it goes anywhere near a client report. If it is in your report, he has seen it and proven it.
The name
Rooted in Wales. Built for global scale.
Tarian is the Welsh word for shield, which is exactly what we are to every client we work with. Labs is how we stay sharp: we research new attack techniques, build our own tooling, and develop capabilities that keep us ahead of what attackers are doing right now.
- Tarian[ tar-ee-an ]Welsh
- Noun: a shield; a means of protection or defence.
- Labs[ labz ]English
- Noun: a place of research, innovation and continuous development.
Proudly Welsh
Headquartered in Wales, entirely UK-owned and operated, and active members of FinTech Wales. As sovereign cyber capability becomes a procurement requirement rather than a preference, our roots matter.
Independent assurance
The Tarian side of our name means shield for a reason. As an independent third party we give you the objective truth about your security posture. No sugar-coating, and no conflict of interest.
Built to stay ahead
The Labs side of our name is not decorative. We research emerging attack techniques, build internal tooling and develop new capabilities, so clients are covered against what is coming next.
What our certifications actually mean.
Plain English. No acronym soup.
- CSTL-INF
Cyber Scheme Team Leader: Infrastructure
The highest UK practitioner-level certification for infrastructure security testing, mandated by the NCSC and the UK Cyber Security Council as a requirement for Principal and Chartered status. Held by our Head of Technical Delivery alongside Principal Cyber Security Professional (PriCSP) registration with the UK Cyber Security Council. If you are procuring security testing under government, defence or regulated contracts, CSTL-INF is what you need to see on the certificate.
- CREST CRT
CREST Registered Tester
CREST is the internationally recognised professional body for offensive security practitioners. CREST Registered Tester is the baseline certification every Tarian Labs practitioner holds. Major banks, financial regulators including the FCA, and many enterprise procurement frameworks recognise it as proof that the person doing the testing meets a defined standard rather than a claimed one.
- OSCP
Offensive Security Certified Professional
The industry benchmark for hands-on penetration testing ability. Unlike multiple-choice exams, OSCP is a 24-hour practical test: candidates must compromise a real set of machines with no assistance. It is widely regarded as one of the most credible certifications for practitioners conducting real-world penetration tests.
- OSEP
Offensive Security Experienced Penetration Tester
An advanced certification focused on evading modern defences and operating inside hardened environments. These are the same techniques used in elite red team engagements. OSEP holders can operate the way a real attacker does: quietly, persistently, and without triggering standard detection controls.
Certifications and registrations
No compromises. No shortcuts.
Four things that are true of every engagement we take on.
Certified at the highest level
Every practitioner holds CREST CRT as a baseline. Our Head of Technical Delivery holds CSTL-INF, PriCSP, OSCP and OSEP on top of that. It means our work holds up under the most rigorous government and enterprise scrutiny.
Deliberate, not reactive
We question assumptions early, cut through complexity, and focus on the vulnerabilities that actually matter. Security that is reactive is security that is already too late.
Always on your side
We are not an annual checkbox. We are a partner invested in your security outcomes. That means staying engaged, translating findings into action, and being straight with you when something needs to change.
Complete discretion
Every engagement is covered by a strict NDA before we begin. What we find stays between us and you. No case studies published without permission, no data retained beyond the engagement, and no exceptions.
Practitioners, not a sales desk.
Tell us what you are worried about and you will get a reply from the person who would run the test, within one business day.